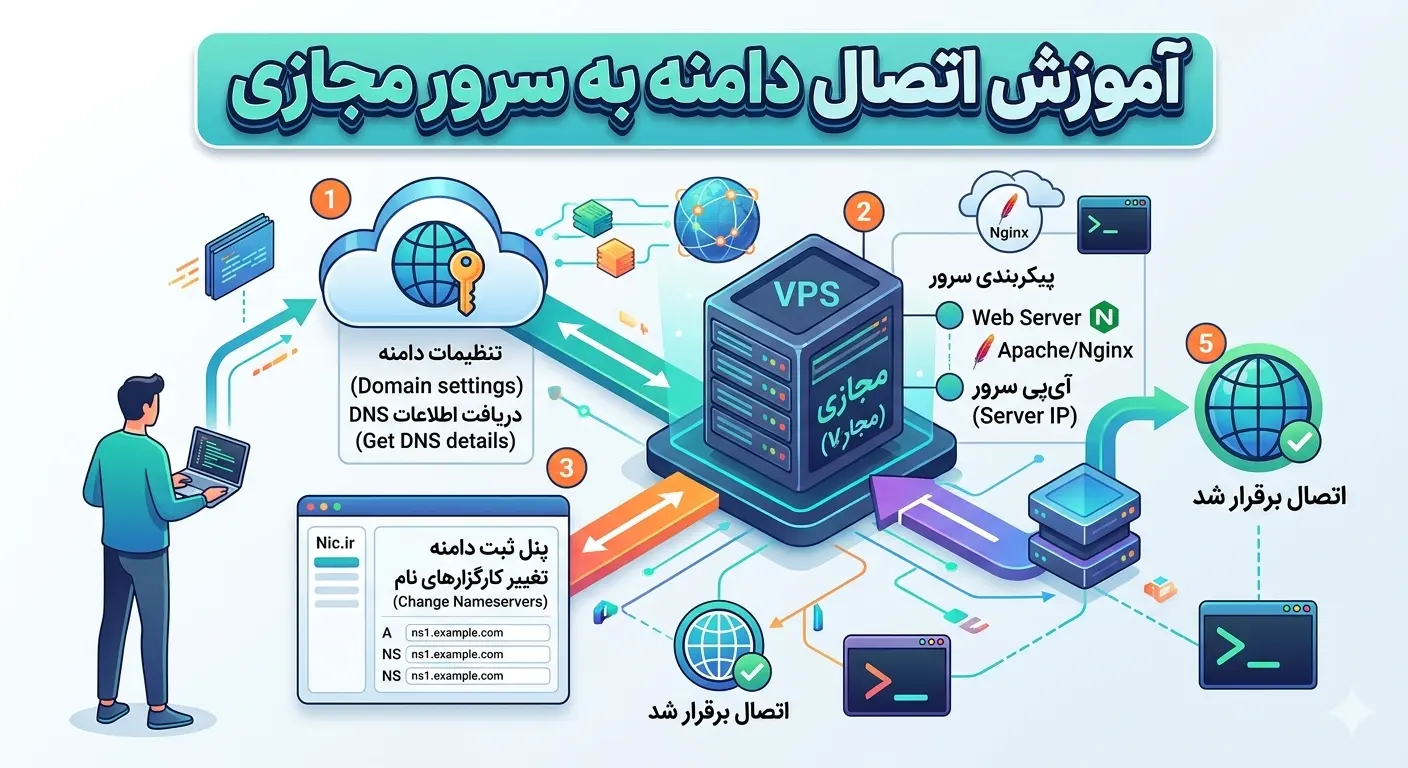
Connecting the domain to the virtual server is one of the most important steps in setting up any website. When you register a domain and provision a virtual server, the two are not yet connected; A domain is just a name and a server is just an IP address. In order for users to reach the content on your server by typing in the domain name, you need to link the two together. In this step-by-step guide, you will learn how to connect the domain to the virtual server, set the necessary records, and configure the web service to respond to the domain.
Prerequisites for connecting a domain to a server
Before starting work, you should have a few things ready. Connecting the domain to the virtual server requires access to both sections so that you can apply the settings in the right place:
- A registered domain: A domain that you own and have access to its DNS management panel.
- An active virtual server: A server with a public IP address on which you can host the site's content.
- Access Domain DNS Management: A panel where you can edit A records and other records.
- SSH access to the server: To install and configure the web server on the virtual server.
If you haven't got a server yet, you can get a suitable server with a dedicated IP by Purchase Virtual Server and then follow the steps below. The IP address of the server is usually announced to you in the server management panel or the delivery email.
Step 1: Find the IP address of the virtual server
The first thing to do to connect a domain to a server is to get the server's public IP address. This address is what the DNS record should point to. You can see the IP of the server from the management panel or by connecting SSH to the server and running the following command:
curl -4 ifconfig.me
# یا
ip addr show
The output of these commands shows the IP address of version 4 of your server; Something like 185.192.112.45. Make a note of this number, as you will need it in the next step. If your server also has a version 6 IP and you want to use it, note it down as well.
Step 2: Set up domain DNS records
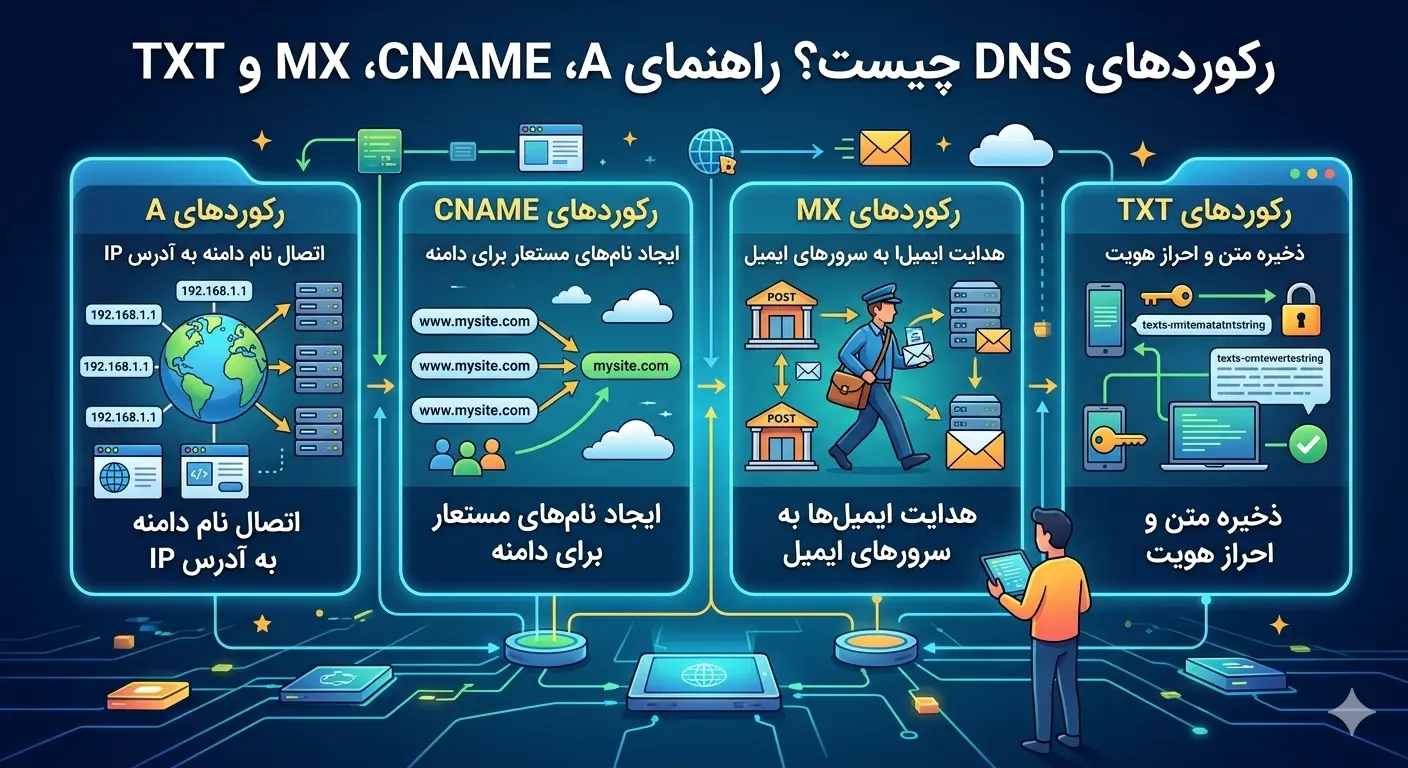
Now you need to go to the domain's DNS management panel and set the A record to point to the server's IP. This is the heart of connecting the domain to the server. Typically, two primary records are defined: one for the main domain and one for the www subdomain.
| type | name | destination | TTL |
|---|---|---|---|
| A | @ | 185.192.112.45 | 3600 |
| A | www | 185.192.112.45 | 3600 |
In the DNS management panel, enter these records exactly as in the table above and replace the IP with the actual address of your server. The @ symbol represents the parent domain itself. Some panels require you to enter the full domain name instead of @. After saving, the changes are gradually propagated to the network.
Record release review
After the record is saved, it may take a few minutes to a few hours for the changes to be applied everywhere. To verify that the domain is pointing to the correct IP, use the following command:
dig yourdomain.com +short
ping yourdomain.com
If the output of these commands shows the same IP as your server, it means that the DNS record has been published correctly and the domain is now pointing to the server. Now you need to prepare the server to respond to this domain.
Note: If you reduce the TTL value to a low number like 300 seconds before setting the new record, subsequent changes will be applied faster. This is very useful during server migration.
Step 3: Configure the web server on the virtual server
DNS connectivity alone is not enough; Your server also needs to know what content to display for this domain. For this, you need to install and configure a web server such as Nginx or Apache. Below is an example of Nginx configuration.
Install Nginx
First, install the web server by connecting to the server via SSH. On Debian and Ubuntu based distributions the commands are as follows:
sudo apt update
sudo apt install nginx -y
sudo systemctl enable --now nginx
Create domain configuration file
Then create a configuration file for your domain so that Nginx knows how to respond to requests for this domain. Create a file in the path /etc/nginx/sites-available/:
server {
    listen 80;
    server_name yourdomain.com www.yourdomain.com;
    root /var/www/yourdomain/public;
    index index.html index.php;

    location / {
        try_files $uri $uri/ =404;
    }
}
Then activate this configuration and reload Nginx:
sudo ln -s /etc/nginx/sites-available/yourdomain /etc/nginx/sites-enabled/
sudo nginx -t
sudo systemctl reload nginx
Now if you open the domain in the browser, the contents of the folder you specified in the root section will be displayed. If your site works with programming languages or content management systems, you should also add settings for them.
Step 4: Activate the SSL certificate
After connecting the domain to the server, be sure to install an SSL certificate so that your site is up with the secure HTTPS protocol. Without SSL, browsers will view your site as insecure and user trust will decrease. The easiest way is to use the free Let's Encrypt tool via Certbot:
sudo apt install certbot python3-certbot-nginx -y
sudo certbot --nginx -d yourdomain.com -d www.yourdomain.com
Certbot will automatically obtain the certificate, update the Nginx configuration, and set up auto-renewal. After this step, your site will be available on HTTPS and the security lock will be displayed in the browser.
Security advice: After enabling SSL, redirect HTTP traffic to HTTPS so that all users are automatically transferred to the secure version of the site. Certbot usually offers this option during installation.
Common domain connection problems and their solutions
Sometimes, after completing the steps, the site does not load. The most common reasons and solutions are: If the domain does not point to the correct IP, the A record is probably not published yet or is registered in the wrong panel; Wait or review the record. If you get a connection error, the server's firewall may be blocking ports 80 and 443; Open these ports. If the default Nginx page is displayed, the domain configuration file is not enabled.
To fix the firewall problem on Ubuntu servers, you can use the following commands:
sudo ufw allow 80/tcp
sudo ufw allow 443/tcp
sudo ufw reload
If you've checked all of these and still have problems, checking the Nginx logs on the /var/log/nginx/error.log path will usually reveal the exact cause. To learn more about domain and DNS settings, you can refer to Rapido Server Articles and if you don't have a domain yet, go to Domain Registration section.
Hosting multiple sites on one server
One of the great advantages of a virtual server is that you can host multiple domains and multiple sites on the same server. This saves costs and simplifies management. For this purpose, each domain must point its A record to the IP of the same server, and in the web server, a separate configuration block should be defined for each domain.
In Nginx, this is done by creating several files in the sites-available folder, each of which has its own server_name and root. For example, you define two different sites like this:
server {
    listen 80;
    server_name site-a.com www.site-a.com;
    root /var/www/site-a/public;
}
server {
    listen 80;
    server_name site-b.com www.site-b.com;
    root /var/www/site-b/public;
}
Based on the server_name value, the web server recognizes which site each request belongs to and displays the correct content. This capability is called Name-based Virtual Hosting and is considered the backbone of shared hosting. Each site can also have its own separate SSL certificate.
Setting up subdomains on the server
In addition to the main domain, it is often necessary to connect subdomains such as blog, store or admin panel to the server. The process is similar to the original domain; First, you create an A record for the subdomain in the DNS panel, and then you create a configuration block for it in the web server.
Type    Name    Value             TTL
A       blog    185.192.112.45    3600
A       shop    185.192.112.45    3600
After publishing these records, you create a server block in Nginx with server_name equal to blog.yourdomain.com and specify the corresponding content folder. This way each subdomain can host a completely independent site or service, while all running on the same server.
Note: When getting an SSL certificate with Certbot, you can add all domains and subdomains with the -d flag in one command to cover them all under one certificate and simplify management.
Performance and security tips after connection
After the domain is successfully connected to the server and the site is up, a few additional steps will help improve speed and security. These are often overlooked but have a huge impact on user experience and site stability.
- Enable compression: Enabling gzip or brotli in Nginx will reduce the size of the data transfer and increase the loading speed.
- Browser cache setting: By defining cache headers for static files, subsequent user visits will be faster.
- Restricting SSH access: Using a key instead of a password and changing the default SSH port increases server security.
- Regular Update: Update system and web server packages regularly to fix security vulnerabilities.
It is also recommended that you take regular backups of your server so that you can restore the site quickly if something goes wrong. Many providers provide automatic snapshots or backups, which are strongly recommended. By following these tips, your site will not only connect to the domain, but also remain fast, secure, and stable.
Monitoring and maintenance after launch
After the domain is connected to the server and the site is up on HTTPS, the administration work begins. In order to keep your site always available and fast, you should regularly monitor the server and domain status. Monitoring helps you identify and fix problems before users notice them.
The most important things to monitor are site availability (uptime), server resource consumption such as CPU and memory, disk space, and SSL certificate expiration date. Although Certbot does the SSL renewal automatically, it's a good idea to make sure it's working properly sometimes. To quickly check the status of services, you can use the following commands:
sudo systemctl status nginx
df -h
sudo certbot certificates
It is also recommended to set up an alert system that will notify you if the site is unavailable or the certificate is about to expire. With regular maintenance and continuous monitoring, the domain connection to your server will not only be established once, but will remain stable and secure in the long run, and your online business will continue to operate without interruption.
Frequently asked questions
Why does my site still not load after setting the A record?
It usually takes up to several hours due to DNS not being fully propagated. Also make sure the web server is installed on the server and configured for the domain and that ports 80 and 443 are open on the firewall.
Do I need a separate server for each domain?
No, a virtual server can host multiple domains. Just create a separate configuration file for each domain on the web server and point the A record of all of them to the IP of the same server. This method is called multi-site hosting.
What is the difference between connecting a domain to an A record and changing a server?
In the A record method, DNS management remains with the registrar and you only specify the destination IP. In the half-server switching method, the entire DNS management is transferred to another server or service, and you have to redefine all the records there.
Is it necessary to install SSL?
Yes, installing SSL is almost mandatory nowadays. Without it, browsers will show the site as insecure, the SEO ranking of the site will decrease and users' trust will be lost. Fortunately, with Let's Encrypt you can get a valid certificate for free.